

F5 Silverline is a cloud-based managed security service designed to protect web applications and application traffic without requiring organizations to operate the entire security infrastructure themselves. Silverline has been associated particularly with managed Web Application Firewall (WAF) and DDoS protection services, combining F5 security technology with security operations and expert policy management.
For organizations evaluating an existing F5 Silverline License, it is important to consider the protected applications, traffic requirements, selected security services, service package, and contract term rather than looking only at the product name.
Benefits of Implementing F5 Silverline
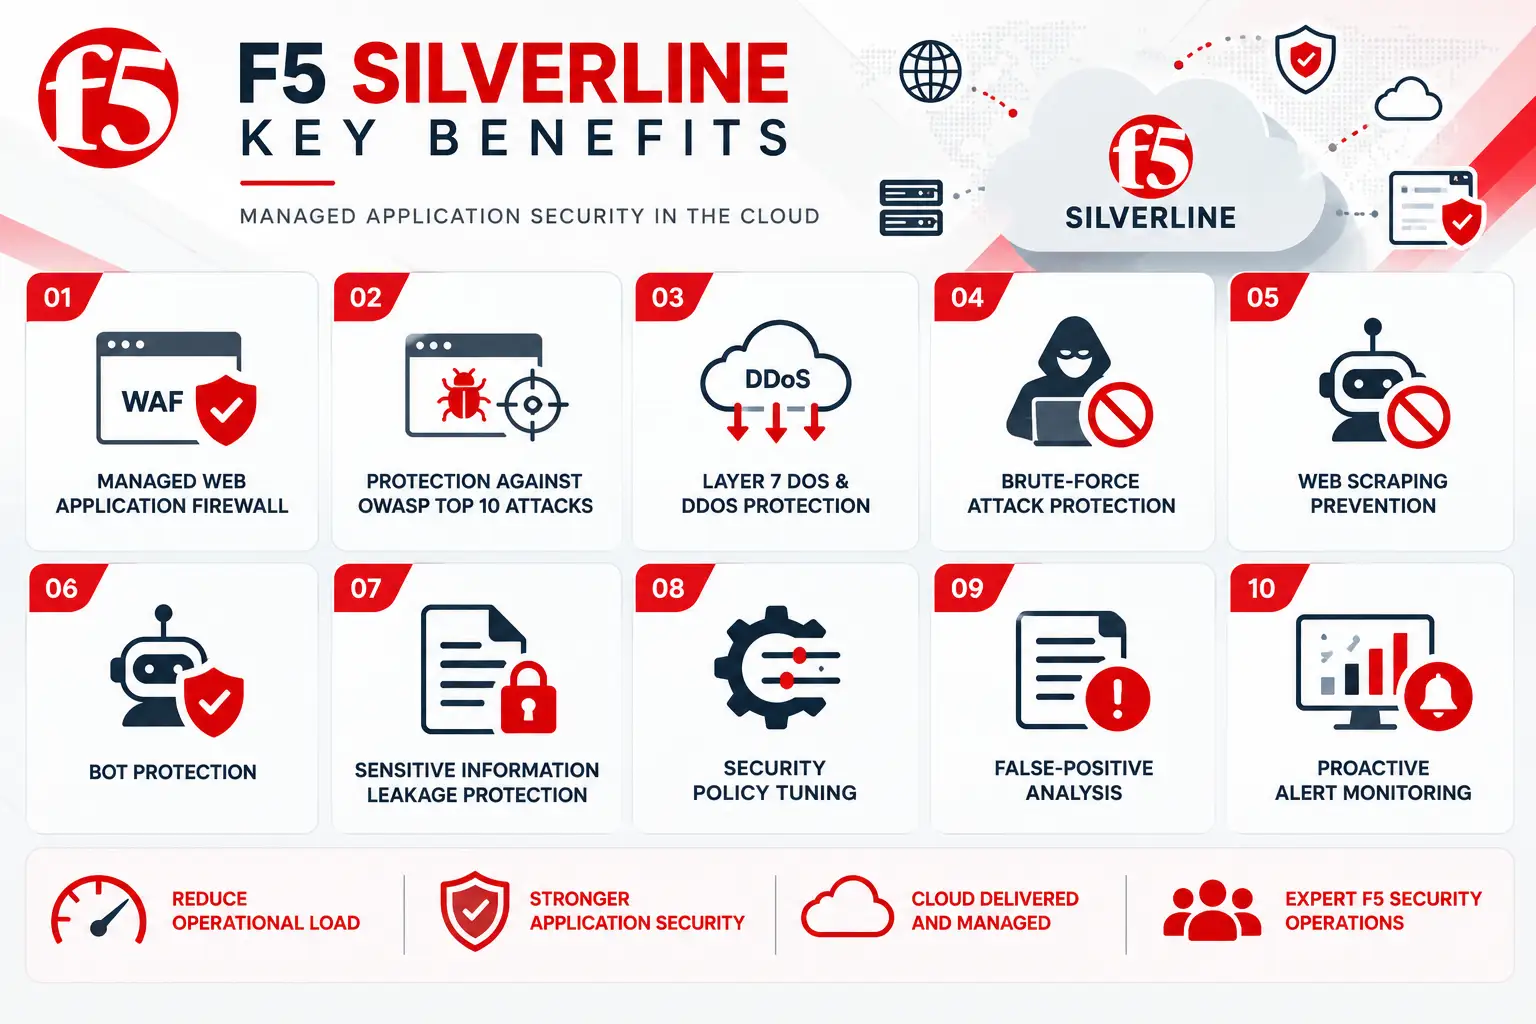
One of the main benefits of Silverline was the ability to consume application security as a managed service rather than operating every WAF function internally. F5’s security operations teams could assist with policy configuration, monitoring, tuning, and investigation, reducing the operational workload for customer security teams.
Other capabilities included:
- Managed Web Application Firewall
- Protection against OWASP Top 10 attacks
- Layer 7 DoS and DDoS protection
- Brute-force attack protection
- Web scraping prevention
- Bot protection
- Sensitive-information leakage protection
- Security policy tuning
- False-positive analysis
- Proactive alert monitoring
How F5 Silverline Works
F5 Silverline operates as a managed cloud security layer in front of protected web applications.
A simplified traffic flow is:
User Request
→ Internet traffic reaches the Silverline security service
Traffic Inspection
→ Requests are inspected against configured application-security policies
Threat Detection
→ Malicious or suspicious requests are identified
Policy Enforcement
→ Allowed requests continue toward the protected application while violating traffic is blocked or handled according to policy
Security Operations
→ F5 security specialists monitor events and tune policies when required
Application Delivery
→ Legitimate traffic reaches the organization’s web application
This managed architecture allowed organizations to outsource significant portions of WAF policy administration while retaining visibility into application-security events.
F5 Silverline Security Capabilities
| Capability | Purpose |
|---|---|
| Silverline WAF | Protect web applications against application-layer attacks |
| Managed Security Operations | Provide policy configuration, monitoring, and tuning |
| DDoS Protection | Mitigate supported denial-of-service attacks |
| OWASP Protection | Detect and block common web application attack techniques |
| Bot Protection | Identify and control automated application traffic |
| Web Scraping Prevention | Reduce unauthorized automated extraction of application content |
| Security Reporting | Provide visibility into attacks and WAF activity |
| PCI Reporting | Support application-security compliance requirements |
F5 Silverline WAF
The Silverline Web Application Firewall was designed to protect web applications from common and advanced application-layer attacks.
Protection included threats such as:
- SQL injection and related web attacks
- Cross-site scripting
- Layer 7 DoS and DDoS
- Brute-force attacks
- Parameter manipulation
- Cookie manipulation
- Request smuggling
- XML-based attacks
F5 Silverline DDoS Protection
Silverline also supported managed DDoS protection services for organizations requiring additional protection against attacks targeting application availability. DDoS protection can address different attack layers, including network and application-level traffic. F5’s broader DDoS portfolio now includes managed cloud protection through Distributed Cloud Services, while legacy Silverline customers have been directed toward the newer platform.
Compatibility & Requirements
Before evaluating an existing Silverline deployment or F5 Silverline License, organizations should review:
- Number of protected applications
- Fully qualified domain names
- Application architecture
- Public-facing services
- On-premises applications
- Cloud-hosted applications
- Expected traffic volume
- SSL/TLS requirements
- WAF policy requirements
- DDoS protection requirements
For organizations planning a new deployment today, the current F5 Distributed Cloud portfolio should also be evaluated because F5 has been transitioning Silverline services toward Distributed Cloud Services.
Pricing and Quote Process
The cost of an F5 Silverline License historically depended on the protected application environment and selected managed security services.
Important quotation factors included:
- Number of protected FQDNs
- Number of applications
- Application traffic
- WAF requirements
- DDoS requirements
- Security operations services
- Required service package
- Support requirements
- Contract duration
F5 Silverline pricing depends on your product edition, license type, deployment model, traffic needs, term, and support requirements.