

Cisco Firewall 9300 is a modular platform within the broader Cisco Security category, designed for data center edge protection, service-provider security, carrier-grade inspection, VPN aggregation, dedicated IPS, and large-scale next-generation firewall deployments. Commonly known through the Cisco Firepower 9300 Series and the Cisco Secure Firewall portfolio, this platform is selected when organizations need chassis-based scalability, high throughput, multiple security modules, flexible interface options, and strong separation between firewall instances or security zones. This page helps buyers understand Cisco Firewall 9300 ordering considerations, review licensing and part-number requirements, and move to the related Cisco Firewall 9300 part numbers for accurate quote planning.
Series Highlights
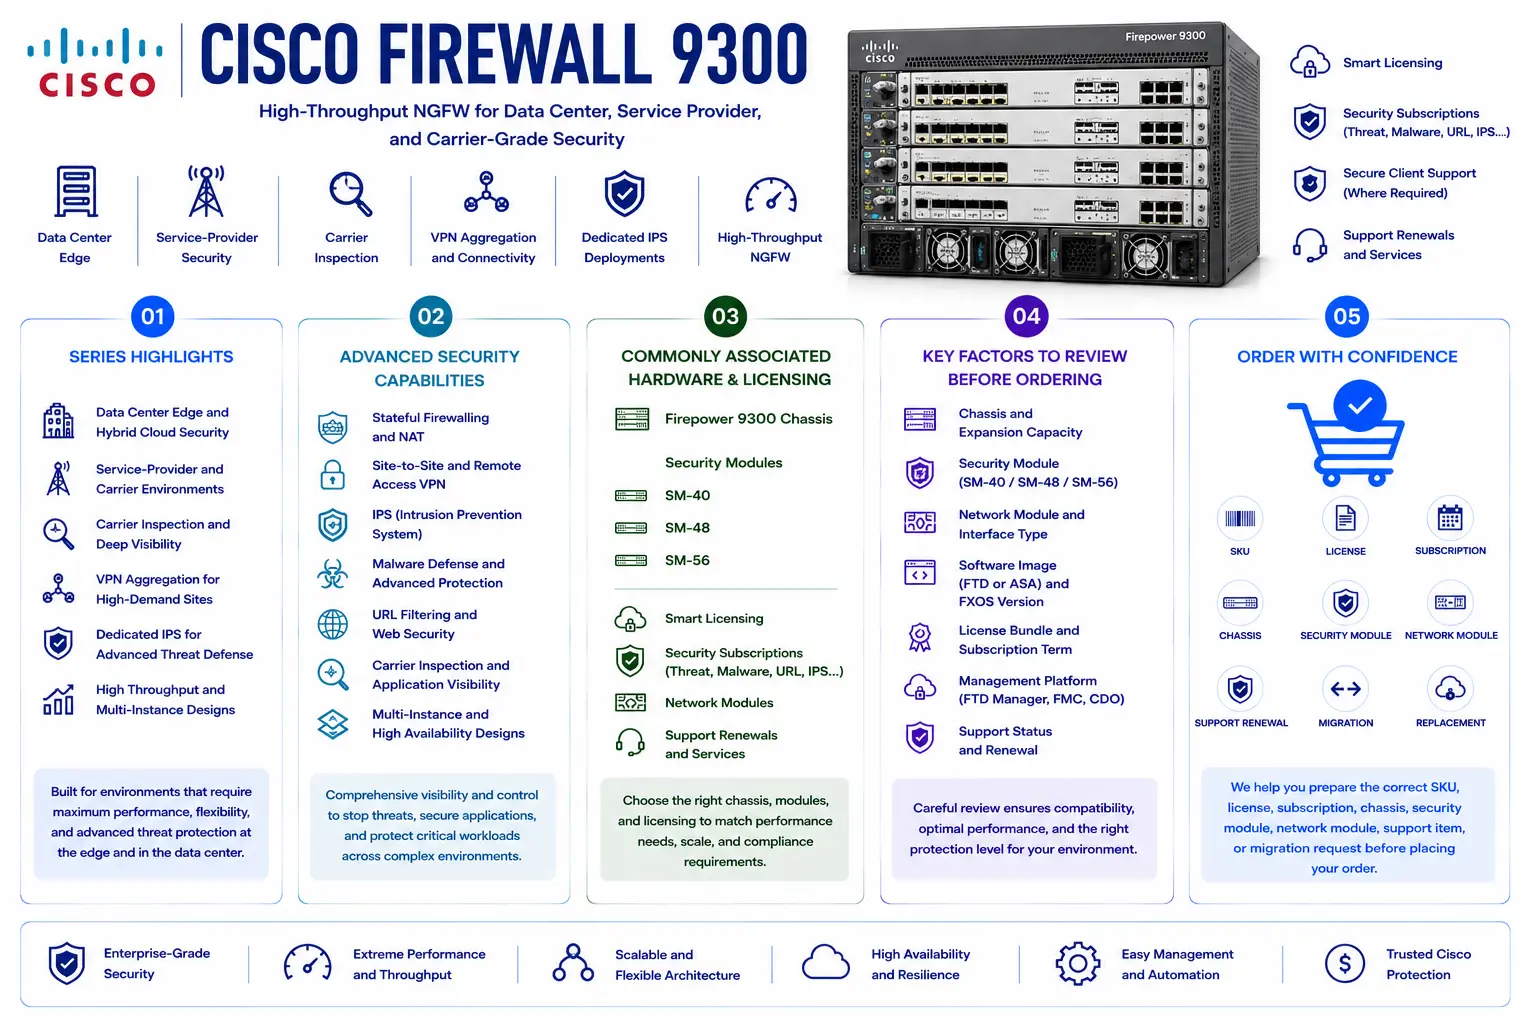
- Suitable for data center edge, service-provider security, carrier inspection, VPN aggregation, dedicated IPS, and high-throughput NGFW deployments
- Supports Cisco Secure Firewall Threat Defense, Cisco Secure Firewall ASA software, FXOS, stateful firewalling, NAT, VPN, IPS, Malware Defense, URL Filtering, Carrier inspection, and multi-instance designs where licensed
- Commonly associated with Firepower 9300 chassis, SM-40, SM-48, SM-56 security modules, network modules, Smart Licensing, security subscriptions, and support renewals
- Requires careful review of chassis, security module, network module, software image, FXOS version, license bundle, subscription term, management platform, and support status
- Helps buyers prepare the correct SKU, license, renewal, subscription, chassis, security module, network module, support item, or migration request before ordering
Review Cisco Firewall 9300 Price List and request a quote tailored to your licensing needs.
Cisco Firewall 9300 At a glance
What it is : Cisco Firewall 9300 is a chassis-based Cisco security platform for high-performance firewall and security service deployments.
Product family : Cisco Firewall License
Typical use : Data center perimeter security, service-provider firewalling, carrier inspection, VPN aggregation, dedicated IPS, multi-instance firewalling, internet-edge protection, ASA deployment, and Threat Defense deployment.
License or ordering scope : Chassis, security module, network module, ASA or Threat Defense image, FXOS version, Smart License, Carrier license, IPS subscription, Malware Defense, URL Filtering, Cisco Secure Client/VPN needs, management platform, support renewal, and subscription term.
Who needs it : Security, network, data center, service-provider, carrier, and infrastructure teams that need the correct Cisco Firewall 9300 part number, security module, license bundle, subscription, network module, support renewal, or replacement item.
Series Overview
Cisco Firewall 9300 is built for environments where firewall performance, modular scale, and operational separation matter. It is commonly deployed in large data centers, service-provider networks, carrier environments, private cloud perimeters, internet-edge security zones, VPN aggregation layers, and inspection-heavy network designs.
In a typical deployment, a Cisco Firewall 9300 chassis can host security modules that run Cisco Secure Firewall Threat Defense or Cisco Secure Firewall ASA software. This makes the platform useful for organizations that need high-throughput firewalling, next-generation inspection, carrier protocol inspection, multi-instance segmentation, or large-scale VPN and perimeter security.
The main value of Cisco Firewall 9300 is chassis-based flexibility. Buyers can plan the security modules, network modules, interface speeds, software image, management platform, license bundle, and support coverage around the real security architecture. Because Cisco Firewall 9300 ordering can involve chassis components, modules, software images, subscriptions, and support contracts, the final part number should be selected after reviewing both the technical design and the operational lifecycle of the environment.
Licensing and Part Number Guidance
Choosing the correct part number for Cisco Firewall 9300 depends on the chassis requirement, security module type, network module, software image, FXOS version, throughput requirement, VPN design, security subscription bundle, management platform, support term, and activation method.
Threat Defense deployments commonly involve Smart Licensing, a base firewall entitlement, and optional subscriptions such as IPS, Malware Defense, URL Filtering, and related threat services. ASA deployments may involve ASA Standard, strong encryption, security contexts, Carrier licensing, VPN-related requirements, Cisco Secure Client needs, and support coverage.
Buyers should confirm whether the request is for a Firepower 9300 chassis, SM-40, SM-48, SM-56, network module, transceiver, subscription renewal, ASA-to-FTD migration, dedicated IPS deployment, HA pair, cluster design, multi-instance design, or support renewal.
The quote should clearly separate chassis SKUs, security modules, network modules, software image, security subscriptions, VPN requirements, transceivers, management needs, accessories, and support contracts.
Common Use Cases
| Use case | Why it matters |
|---|---|
| Data center perimeter security | Protects high-volume traffic between users, applications, servers, partners, and internet-facing services |
| Service-provider firewalling | Supports large-scale security designs where throughput, interface density, and carrier-grade inspection matter |
| Carrier inspection | Helps validate Diameter, GTP/GPRS, SCTP, and related carrier protocol inspection requirements where licensed |
| Multi-instance firewalling | Allows separate logical firewall instances for different tenants, zones, or operational teams |
| Dedicated IPS deployment | Supports inspection-focused designs where the platform is used mainly for intrusion prevention |
| VPN aggregation | Supports site-to-site VPN, remote access planning, Cisco Secure Client needs, and encryption requirements |
Models, Licenses, and Ordering Scope
| Area to check | What to confirm |
|---|---|
| Chassis | Exact Cisco Firepower 9300 chassis requirement and power option |
| Security module | SM-40, SM-48, SM-56, number of modules, performance target, and compatibility |
| Network module | 1G, 10G, 40G, 100G interface needs, module type, transceivers, and port plan |
| Software image | Cisco Secure Firewall Threat Defense or Cisco Secure Firewall ASA software |
| Platform software | FXOS version, software compatibility, upgrade path, and supported deployment mode |
| Security services | IPS, Malware Defense, URL Filtering, Security Intelligence, file control, application visibility, Carrier, or dedicated IPS mode |
| VPN requirement | Site-to-site VPN, remote access VPN, Cisco Secure Client licensing, strong encryption, and user scale |
| Management platform | Firewall Management Center, Cisco Defense Orchestrator, Security Cloud Control, or ASA management workflow |
| License type | Base firewall entitlement, Smart License, Threat subscription, Malware Defense, URL Filtering, Carrier, ASA, security contexts, or support renewal |
| Part number | Correct Cisco Firewall 9300 chassis SKU and related security module, network module, license, subscription, renewal, support, or accessory item |
What to Check Before Requesting a Quote
Before requesting a quote for Cisco Firewall 9300, confirm the chassis requirement, security module type, number of modules, software image, FXOS version, required throughput, interface speed, network module need, VPN requirement, security subscriptions, management platform, support term, and Smart Account status.
You should also define whether the request is for a new chassis, module expansion, HA pair, cluster, multi-instance firewall design, dedicated IPS deployment, subscription renewal, ASA-to-FTD migration, Carrier inspection, Cisco Secure Client requirement, support renewal, spare module, or replacement project. Each case can change the final SKU and licensing scope.
For existing environments, prepare the current inventory first. This should include chassis serial number, installed security modules, network modules, transceivers, software image, FXOS version, current license status, enabled subscriptions, management platform, VPN usage, support coverage, and renewal date.
Activation and Delivery Notes
After the correct Cisco Firewall 9300 part number is selected, activation depends on the software image, Smart Account, license type, FXOS version, management platform, and subscription bundle. Many Cisco Secure Firewall Threat Defense deployments use Smart Licensing or Smart Licensing Using Policy for entitlement visibility and reporting. Subscriptions such as IPS, Malware Defense, URL Filtering, and Carrier should match the number of appliances, modules, or supported instances according to the selected licensing model.
For hardware delivery, compatibility should be checked before shipment. Chassis, security modules, network modules, transceivers, power option, software image, FXOS version, management platform, encryption requirement, and support coverage should match the planned security design. For renewals, replacements, or migrations, review the current license and support status first. This helps prevent ordering delays and keeps the selected SKU aligned with the real security requirement.
Cisco Firewall pricing depends on your license type, deployment model and support requirements.