

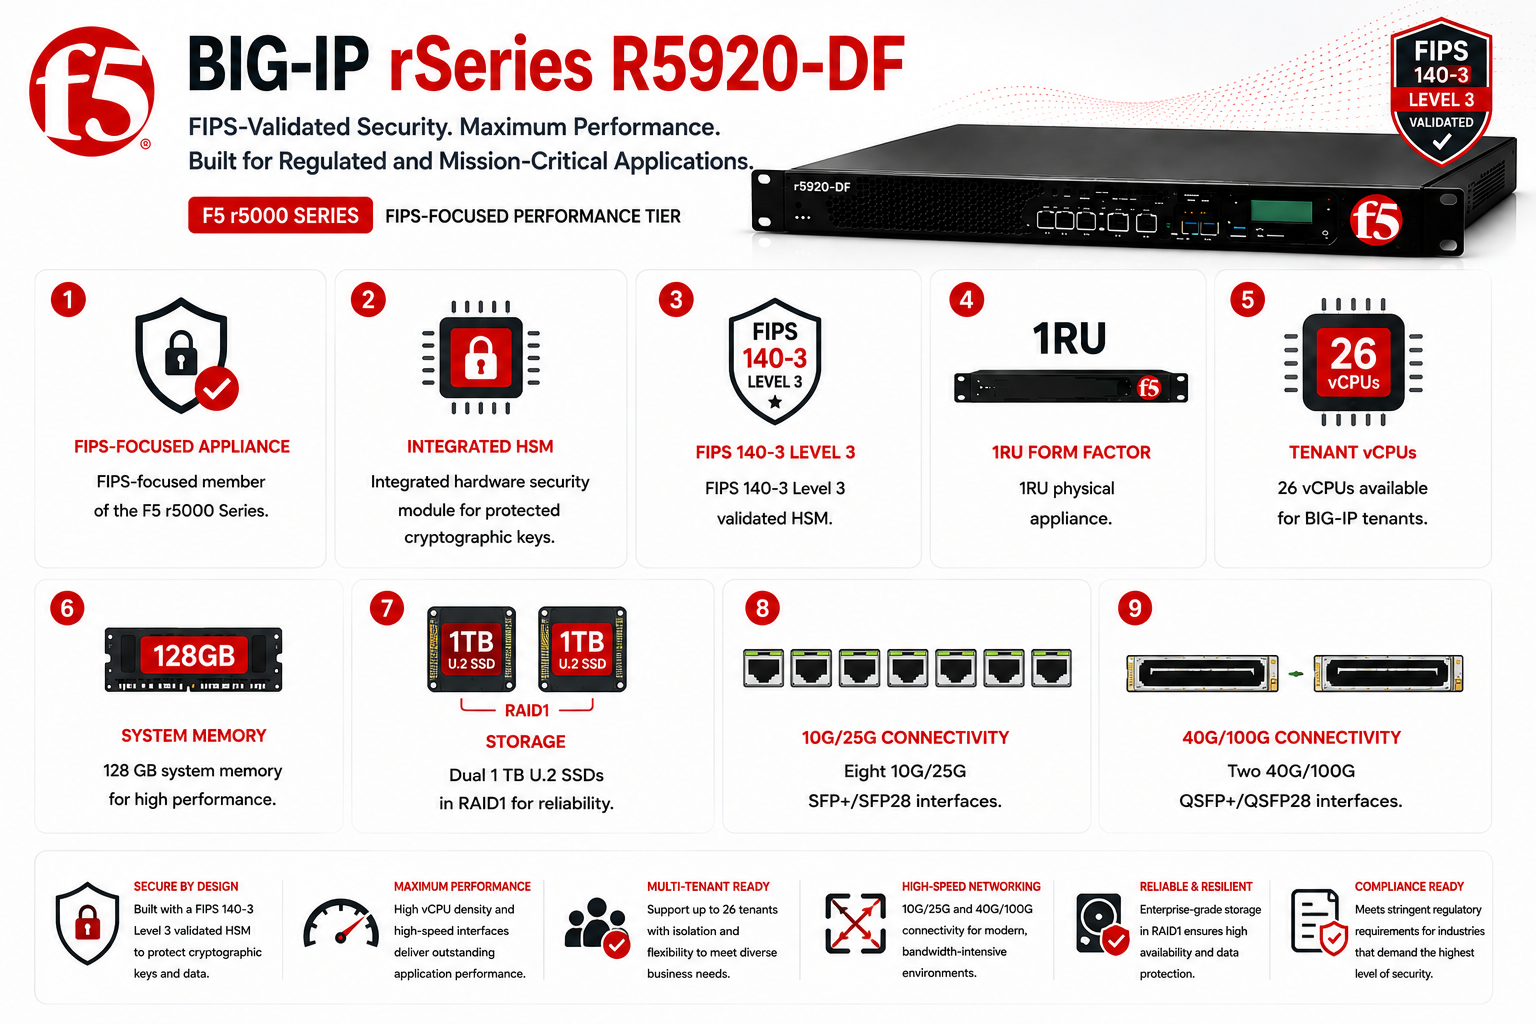
BIG-IP R5920-DF is the FIPS-focused model in the F5 r5000 Series, designed for environments where application delivery and security must be combined with hardware-protected cryptographic key storage. It uses the same general r5000 performance class as R5900, but adds an integrated hardware security module (HSM) and redundant internal storage, making it particularly relevant to government, financial, healthcare, and other regulated environments with stricter cryptographic requirements.
The platform provides 26 vCPUs for BIG-IP tenant workloads, 128 GB of memory, 25G and 100G interfaces, and an integrated FIPS HSM. Unlike R5600 and R5800, however, R5920-DF is not a Pay-as-you-Grow model. It should be selected because FIPS-protected key handling is part of the design, not simply because more r5000 performance is required.
Series Highlights
- FIPS-focused member of the F5 r5000 Series
- Integrated hardware security module for protected cryptographic keys
- FIPS 140-3 Level 3 validated HSM
- 1RU physical appliance
- 26 vCPUs available for BIG-IP tenants
- 128 GB system memory
- Dual 1 TB U.2 SSDs in RAID1
- Eight 10G/25G SFP+/SFP28 interfaces
- Two 40G/100G QSFP+/QSFP28 interfaces
Review BIG-IP R5920-DF Price List and request a quote tailored to your licensing needs.
BIG-IP R5920-DF At a glance
What it is: FIPS-capable r5000 Series application delivery and security appliance
Product family: BIG-IP rSeries License
Platform layer: F5OS
Compute: 32 total vCPUs; 6 reserved for F5OS and 26 available to tenants
System memory: 128 GB
Storage: Dual 1 TB U.2 SSDs configured as RAID1
FIPS capacity: Up to 24 FIPS partitions
Interfaces: Eight 10G/25G ports plus two 40G/100G ports
Series Overview
The R5920-DF contains 16 physical CPU cores presented as 32 vCPUs through hyperthreading. Six are dedicated to the F5OS platform layer, leaving 26 vCPUs for BIG-IP tenants. In that respect, its tenant compute capacity is comparable to the fully enabled R5900.
The important difference is cryptography. R5920-DF includes an embedded HSM designed to protect private keys and perform cryptographic operations inside dedicated hardware. F5 currently lists the integrated NITROX III module used by R5920-DF under FIPS 140-3 Level 3 validation certificate 4700. F5 also explicitly notes that this Level 3 validation applies to the integrated HSM, not to the entire BIG-IP system.
Storage is another difference from standard r5000 appliances. Where R5600, R5800, and R5900 normally use a single SSD, R5920-DF includes two 1 TB U.2 SSDs in a RAID1 configuration, adding disk redundancy for this security-focused platform.
Licensing and Part Number Guidance
An R5920-DF order should begin with the compliance requirement. If the project does not require an integrated FIPS HSM, a standard R5900 may provide similar tenant compute with a simpler commercial model. Where protected cryptographic keys are required, the R5920-DF platform is then combined with the appropriate BIG-IP License services, such as traffic management, application security, DNS, access, or network-security capabilities.
FIPS resources introduce another sizing layer. The integrated HSM supports up to 24 FIPS partitions on the r5000-DF platform. F5 allows administrators to allocate key capacity and hardware acceleration devices among those partitions, which can then be associated with individual BIG-IP tenants. There is no R5920-DF PAYG tier. F5 specifically identifies R5920-DF and R10920-DF as FIPS platforms without Pay-as-you-Grow options.
Common Use Cases
| Use case | Why R5920-DF can fit |
|---|---|
| Regulated application delivery | Combines BIG-IP ADC services with hardware-protected keys |
| TLS termination | Keeps private-key operations inside an integrated HSM |
| Application security | Supports BIG-IP security services with FIPS-oriented cryptography |
| Government environments | Designed for deployments with formal FIPS requirements |
| Financial services | Hardware key protection for sensitive application infrastructure |
| Multi-tenant FIPS | Separate HSM partitions can be assigned to BIG-IP tenants |
| iSeries FIPS refresh | Current replacement path for older i5820-DF / i7820-DF environments |
| HA deployment | Two systems can provide BIG-IP tenant-level redundancy |
F5 introduced R5920-DF and R10920-DF as the rSeries replacement options associated with the retirement of the older i5820-DF and i7820-DF platforms.
Models, Licenses, and Ordering Scope
| Area | What to confirm |
|---|---|
| Platform | BIG-IP R5920-DF |
| Compliance | Whether integrated FIPS HSM is actually required |
| BIG-IP services | LTM, Advanced WAF, DNS, AFM, APM, or required combination |
| Tenant design | Tenant quantity, vCPU, memory, and BIG-IP role |
| FIPS partitions | Number of tenants requiring HSM access |
| Key capacity | Cryptographic key requirements per partition |
| Interfaces | 10G, 25G, 40G, or 100G |
| Storage | Dual 1 TB RAID1 architecture |
| Availability | Standalone or paired HA deployment |
| Power | AC or supported DC configuration |
| Optics | SFP+, SFP28, QSFP+, or QSFP28 |
| Support | F5 service level and term |
| Part numbers | Appliance, BIG-IP entitlement, optics, power, support, and accessories |
What to Check Before Requesting a Quote
The first question should be why FIPS hardware is required. If a policy, customer contract, government standard, or security architecture specifically requires private keys to remain inside a validated HSM, R5920-DF is materially different from R5900. Next, document the applications and cryptographic workload. Include expected traffic, TLS transactions, key quantity, tenant count, BIG-IP modules, security inspection, interface speeds, and HA requirements.
FIPS partition planning deserves particular attention. F5 documents up to 25,475 keys for the R5920-DF HSM and up to 32 acceleration devices, but these resources need to be distributed across the FIPS partitions created for tenants. If the environment needs more than the available r5000-DF compute, HSM resources, or tenant scale, compare R10920-DF rather than looking for a PAYG upgrade that does not exist.
Activation and Delivery Notes
R5920-DF is configured through the F5OS platform layer. In addition to normal rSeries networking and license activation, the HSM must be initialized before FIPS partitions are created and assigned to BIG-IP tenants.
F5 currently requires BIG-IP 17.1.0.1 or later for tenants using the rSeries FIPS platform. After the HSM is initialized, administrators can allocate keys and acceleration resources to individual partitions and associate those partitions with tenants.
For migrations from older iSeries FIPS appliances, F5 also provides an HSM-partition backup option intended to support secure key migration workflows.
Before shipment, confirm the precise FIPS requirement, BIG-IP entitlement, optics, power model, HA quantity, support term, and software compatibility.
F5 pricing depends on your product edition, license type, deployment model, traffic needs, term, and support requirements.